Uptime Kuma is a free open source monitoring tool and notification engine to keep you informed about your critical servers and services. In this post, I will perform a complete setup of Uptime Kuma on Digital Ocean with Docker, and we’ll tighten it down for security. Let’s get started!
Part 1: Server Setup
For this tutorial, we’re going to use a Digital Ocean droplet with Docker. This is a quick and easy way to get this project started, and Uptime Kuma works fine even on the smallest $6/month droplet.
*** NOTE: Uptime Kuma is a monitoring engine, but it’s not magical. It can only monitor what it can ‘see’, meaning that if you’re installing Uptime Kuma in a Digital Ocean droplet as I am doing in this tutorial, Uptime Kuma will only be able to monitor services and servers/IP’s that are exposed to the Internet. You could also install Uptime Kuma on bare metal, or in a Docker container somewhere else in your LAN to give it the ability to see internal resources. Wherever you install Uptime Kuma, just keep this in mind.
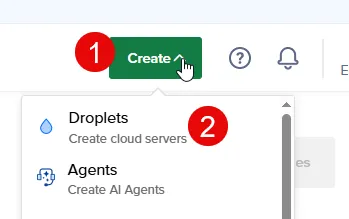
Log into Digital Ocean and click the green ‘Create’ button in the upper right-hand corner, then choose Droplets.
*** NOTE: If you have found this tutorial helpful, and are just signing up for Digital Ocean, use my referral link! Anyone who uses my referral link gets $200.00 worth of Digital Ocean credit over 60 days, and I get a few bucks worth of credit as well. Thanks!
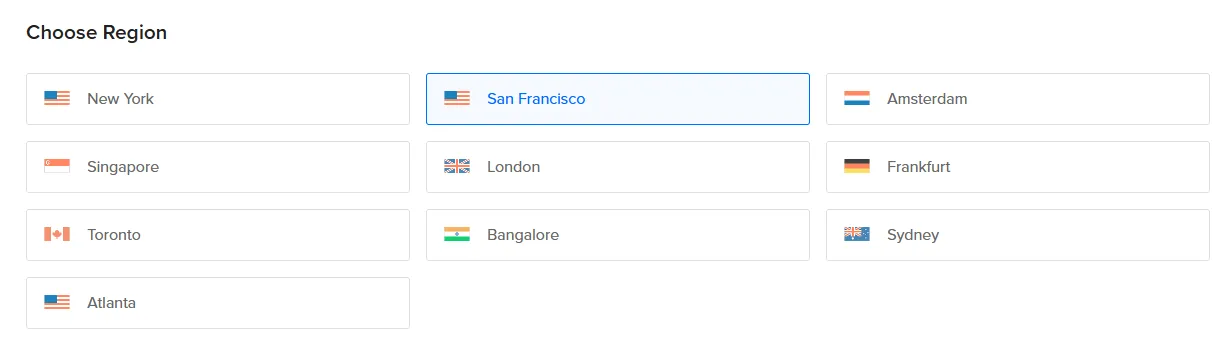
Pick a region close to you:
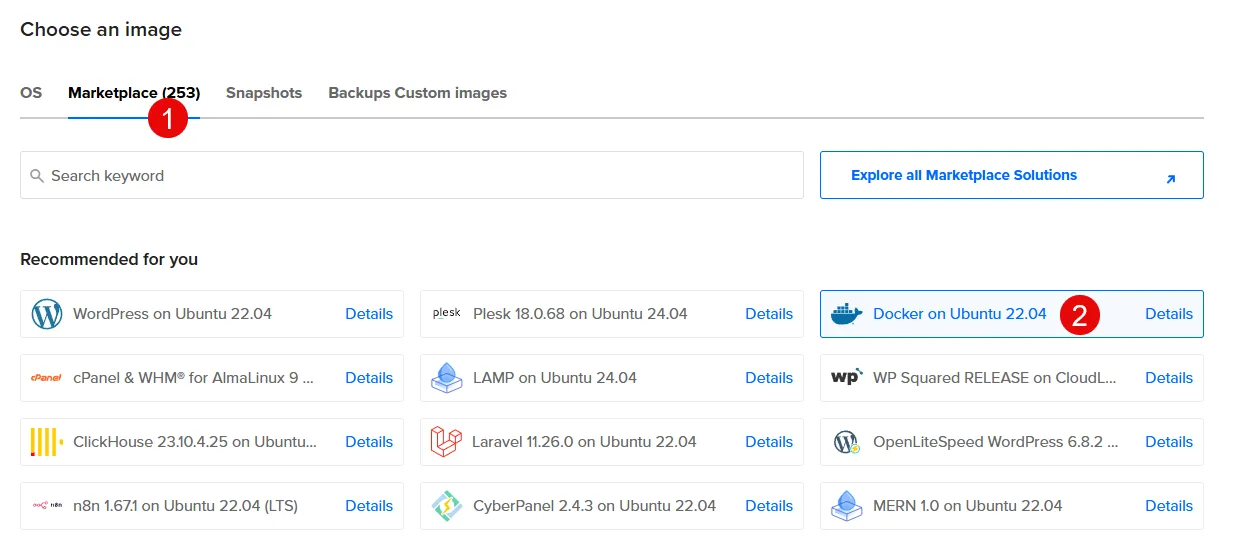
Then scroll down to ‘Choose an image’ and click on the ‘Marketplace’ tab. Select ‘Docker on Ubuntu 22.04’ as the image you want to use.
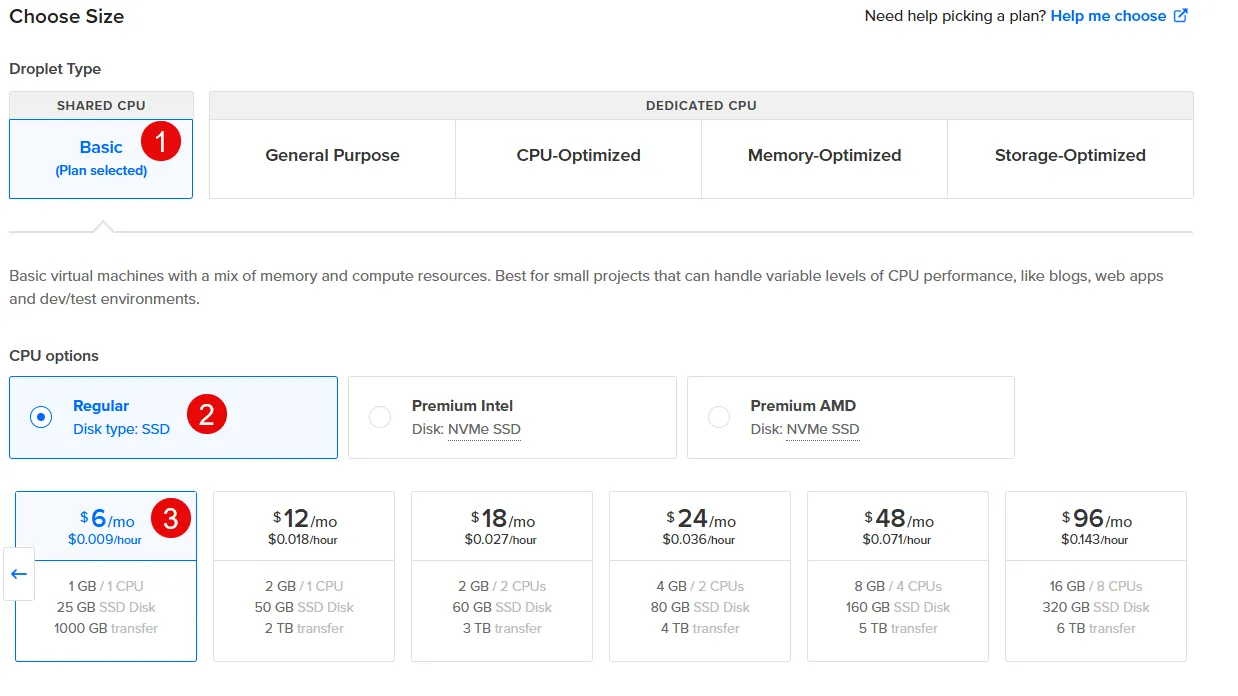
Scroll down further and choose your droplet size: the $6.00/month droplet is fine for basic monitoring, but you may want to increase the droplet size for larger deployments to account for log file storage.
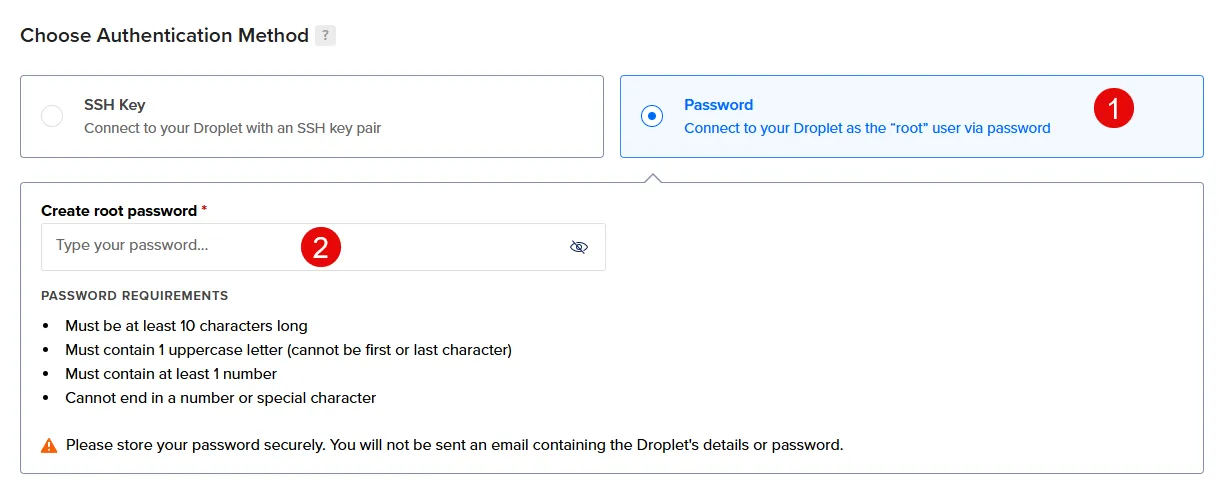
For Authentication Method, choose password (you can also do SSH key if you’d like to be a bit more secure, however I am not detailing that process as part of this tutorial). Create a strong ‘root’ user password.
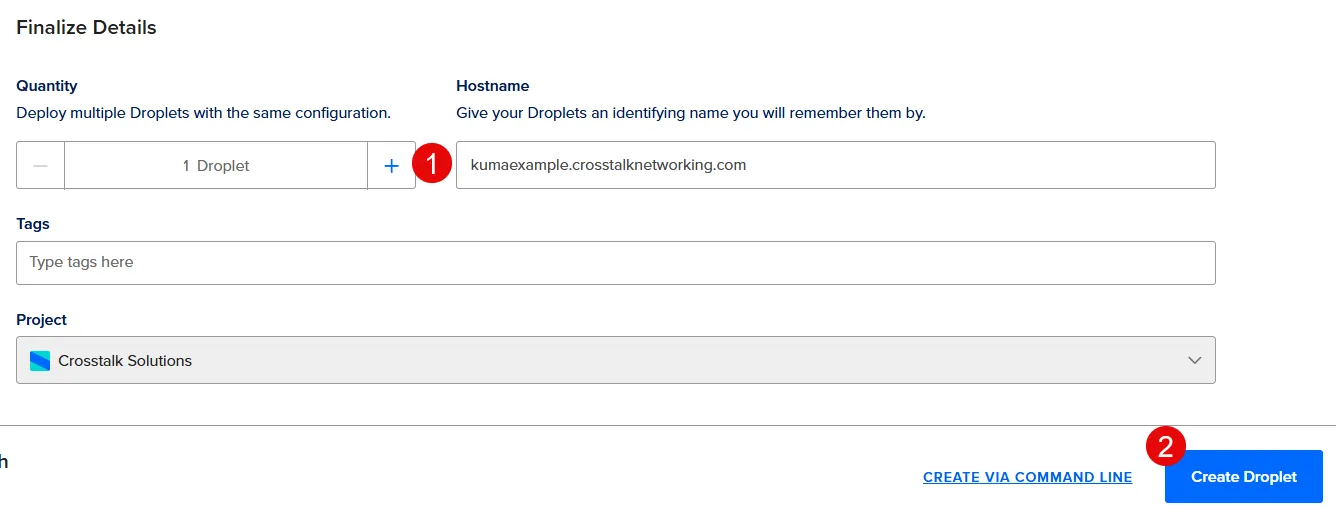
Finally, give your server a hostname and click ‘Create Droplet.’
Your server will now be created. Note down the IP address that your droplet receives.

Part 2: Add FQDN
You’ll need to create a DNS A-Record for your new droplet. To do so, log into your DNS provider (I use Cloudflare) and add an A-record. Give it the hostname that you used when creating your droplet and paste in the IP address.
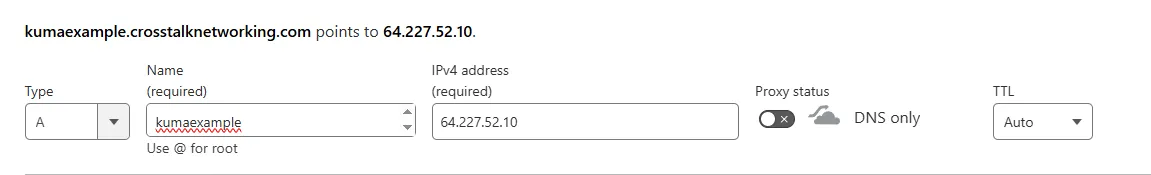
Best to do this now since DNS can often take a bit to propagate.
Part 3: Server Updates and Kuma Install
Use SSH to log into your Uptime Kuma server using user ‘root’ and the password that you set during droplet creation.
Run the following to update the server to the latest and greatest (should only take a minute or two):
sudo apt update && sudo apt upgrade -y*** NOTE: If you want to take the EASY way out: you can technically now install Uptime Kuma with a single line:
docker run -d --restart=always -p 3001:3001 -v uptime-kuma:/app/data --name uptime-kuma louislam/uptime-kuma:1HOWEVER, there are a few issues with this. First of all, you’re running on a non-standard port (3001), and we want to lock everything to standard HTTPS 443 for ease of administration. Second, this is a single docker command/container. If you ever want to add additional Docker containers using a Docker compose file, this single command does not achieve that goal. So again, if this is a locally hosted instance of Uptime Kuma, it’s the only Docker container you’re ever gonna have on the server, and you don’t care that it’s on a non-standard port, then by all means, run the command above and you’re all done. BUT, if you want to do a bit more of an advanced and comprehensive installation, proceed with the following commands.
We’re going to install a couple of Docker containers here: Uptime Kuma (of course) as well as Caddy which gives us a simple way to redirect HTTPS port 443 to our Uptime Kuma Docker instance running on port 3001. This way, when you browse to the Uptime Kuma interface, you don’t have to remember that it’s running on port 3001.
Start by creating a folder for our Docker compose file:
mkdir uptime-kuma-proxy
cd uptime-kuma-proxy
Now let’s create a file that tells Caddy how we want to redirect:
nano -w CaddyfileInside that file, paste the following:
status.yourdomain.com {
reverse_proxy uptime-kuma:3001
}
Replace ‘status.yourdomain.com’ with your actual Uptime Kuma FQDN (A-record) that you created earlier. CTRL+X followed by Y to save and exit.
Now create a Docker compose file:
nano -w docker-compose.ymlCopy/paste the following into the Docker compose file:
services:
  uptime-kuma:
    image: louislam/uptime-kuma:1
    container_name: uptime-kuma
    volumes:
      - uptime-kuma:/app/data
    restart: always
    networks:
      - caddy_network

  caddy:
    image: caddy:2.7-alpine
    container_name: caddy
    restart: unless-stopped
    ports:
      - "80:80"
      - "443:443"
    volumes:
      - ./Caddyfile:/etc/caddy/Caddyfile
      - caddy_data:/data
    networks:
      - caddy_network

volumes:
  uptime-kuma:
  caddy_data:

networks:
  caddy_network:
    driver: bridge
*** NOTE: This is a YAML file, so the syntax has to be EXACT or else it’ll error out
CTRL+X followed by Y to save and exit.
Now start everything up!
docker compose up -d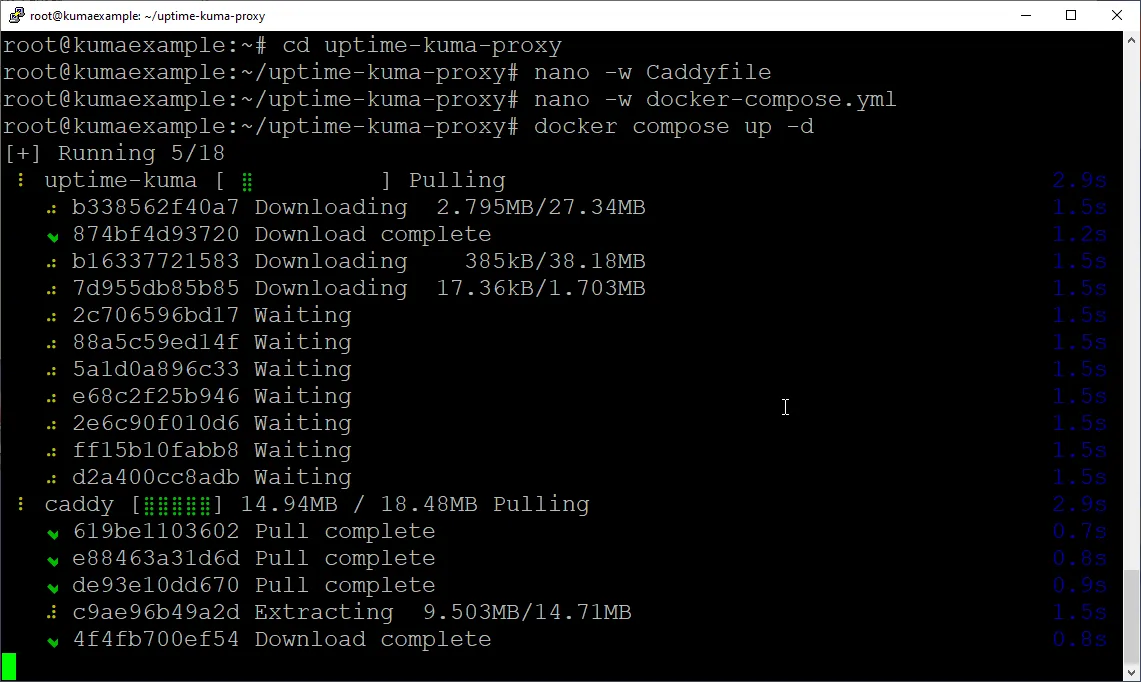
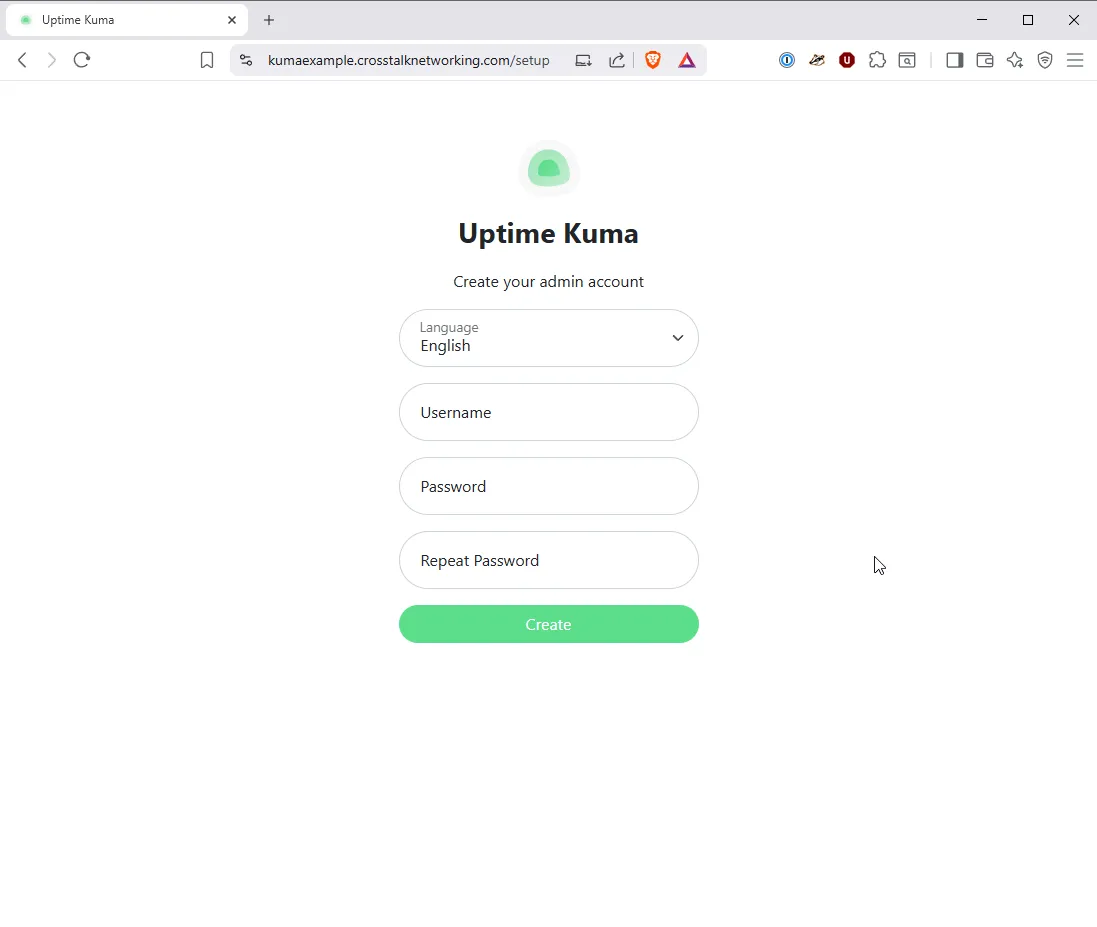
This should only take about 30 seconds or less, and now your Uptime Kuma instance should be up and running when you browse to the FQDN, and it should have a valid Let’s Encrypt certificate!
Part 4: Uptime Kuma initial setup
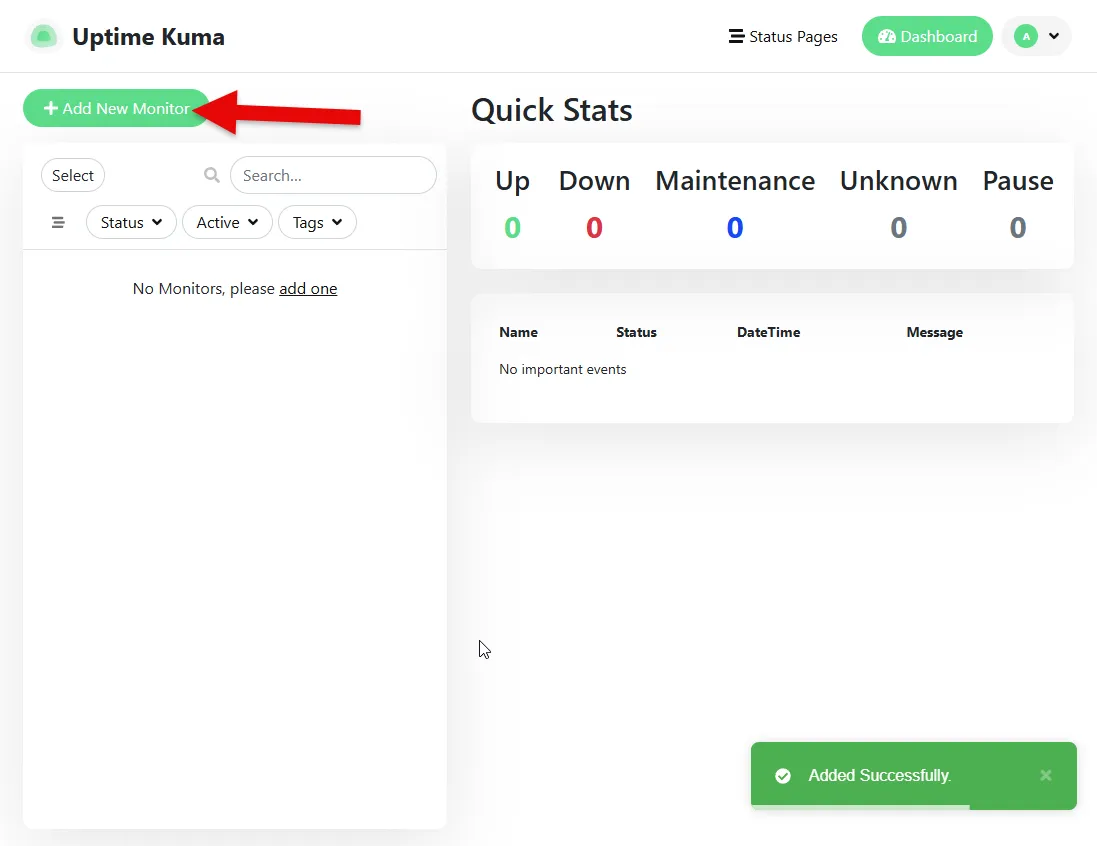
Give your Uptime Kuma instance an Admin username and password and then click ‘Create.’ You’ll be redirected to the Uptime Kuma dashboard. From here, click ‘Add New Monitor.’
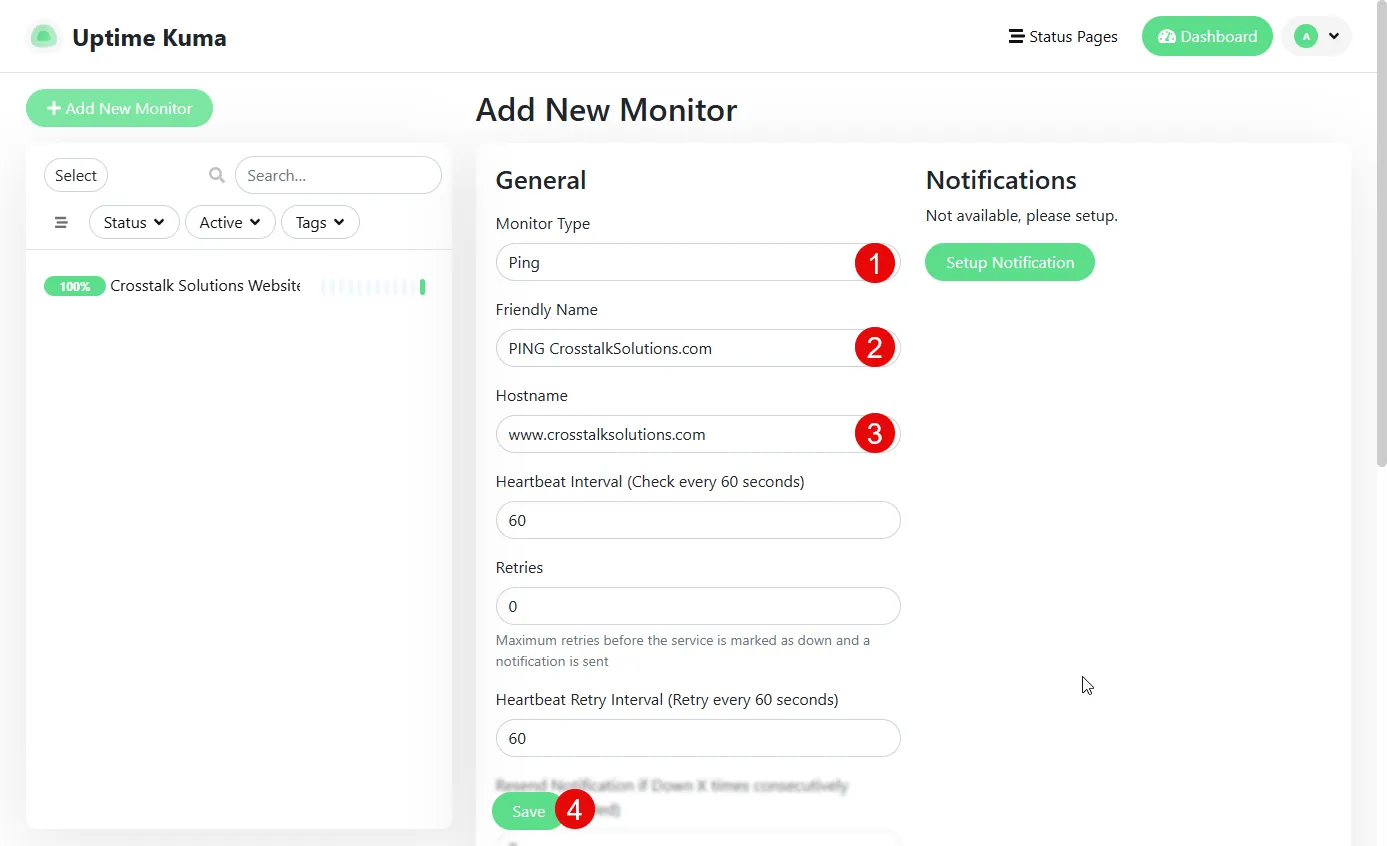
Let’s add a simple HTTPS monitor for checking to see if a website is online. For Monitor Type, choose HTTP(s). Add whatever you want for ‘Friendly name’ and then enter in the URL of the website you wish to monitor. Click ‘Save’ to save the monitor.
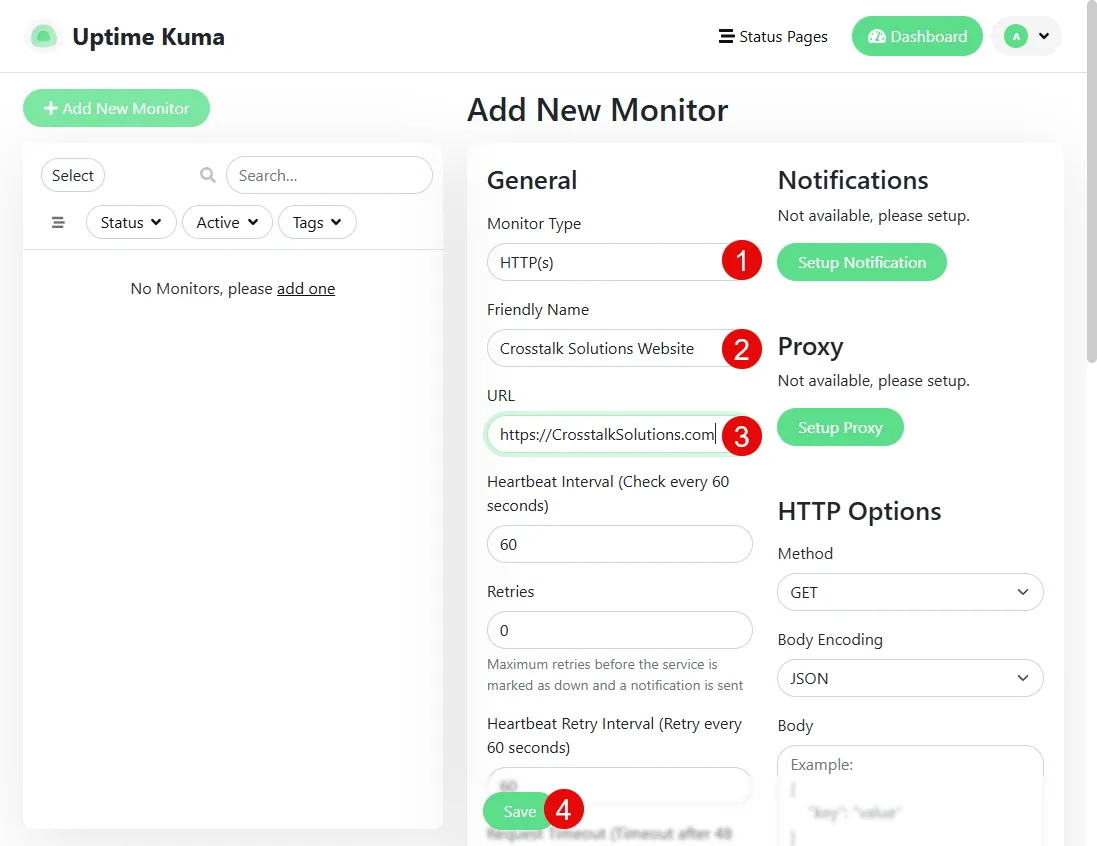
That’s it! You’re now monitoring a website. Let’s add a PING test as well. Same process as the HTTP(s) monitor, but change the Monitor Type to ‘Ping.’
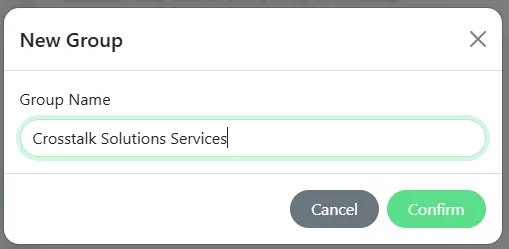
If you edit your new monitors, you can even create a group for them. Under Advanced, click the ‘+’ sign next to Group to add a new group, and then Confirm > Save.
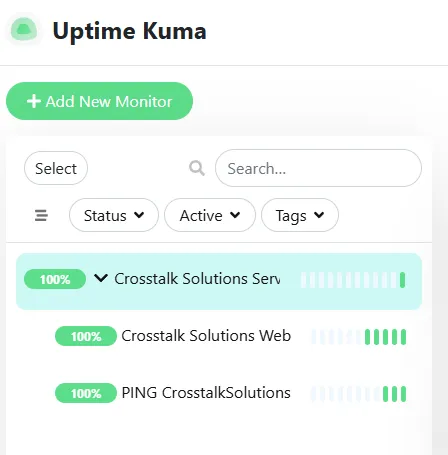
Adding to groups just keeps stuff cleaner on the dashboard if you’re monitoring a bunch of services.
So now that we have monitors, we need to set up our notifications! Edit one of your monitors and then click the ‘Setup Notification’ button on the right-hand side.
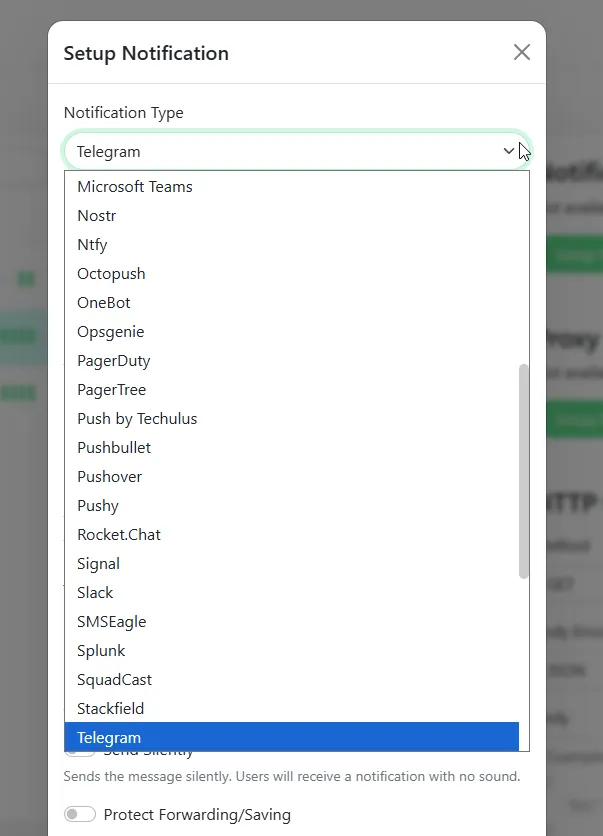
Click on Notification Type and scroll through the vast amount of notifications available to you!
I’m going to set up a Discord notification. First, in Discord, I create a new Text channel called #uptime-kuma (give it whatever permissions for whomever needs to see the alerts). Then I click on ‘Integrations’ and create a new webhook. Once the webhook is created, I copy the webhook URL.
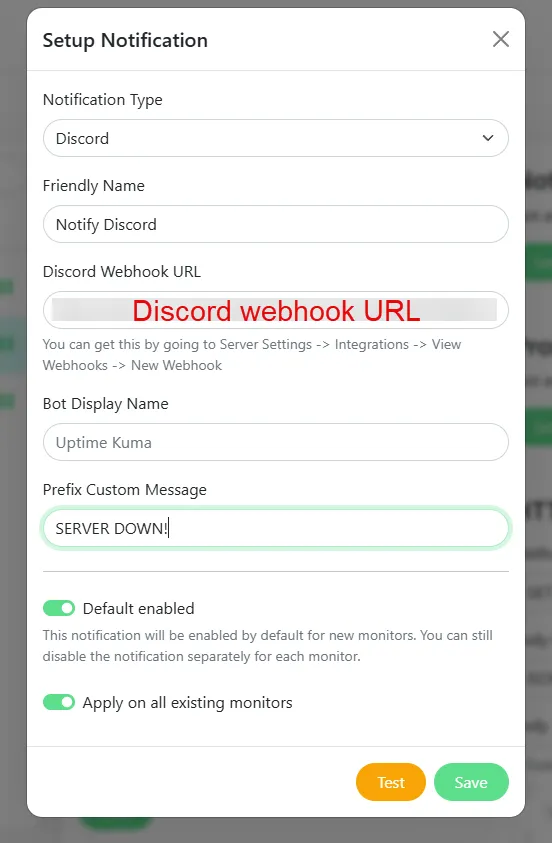
Head back to Uptime Kuma. In the Setup Notification window, choose Discord, give it a friendly name, and then paste in the Discord webhook. You can also add a prefix for server down messages, and choose whether you want this notification to be default for all new monitors, and whether to add this notification to all existing monitors. Click ‘Test’ to test it out.
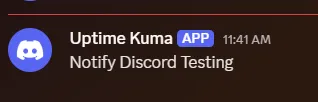
If you’ve done everything correctly, you should see a test notification pop up in Discord.
Click ‘Save’ and you’re all set! Most of the other notifications are configured similarly, so scroll through the list and figure out which of the notifications are right for you.
Finally, let’s create a status page for our monitors. Click ‘Status Pages’ in the upper right-hand corner followed by ‘New Status Page.’
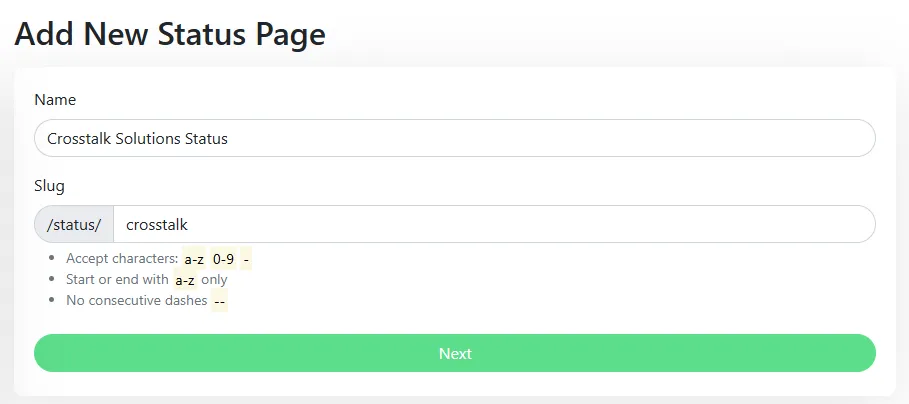
You can give the status page a friendly name and optionally append a slug if you have multiple status pages that you want to create. Click ‘Next.’
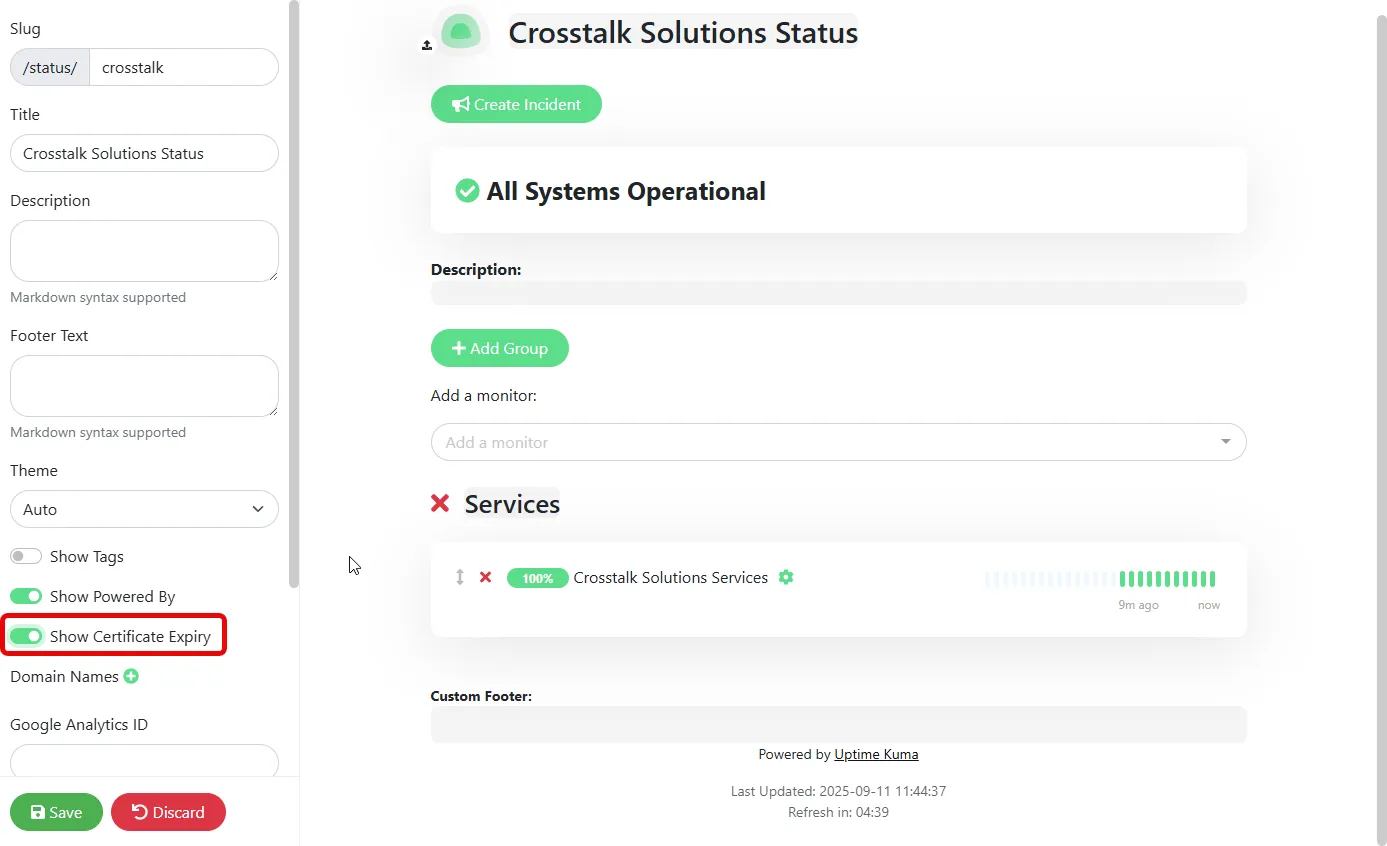
Now you can add monitor groups or individual monitors to the status page. For HTTP(s) monitors, you can even toggle on the Show Certificate Expiry option to let you know how many days are left on that server’s secure cert. Click ‘Save’ and you can now browse to that status page.
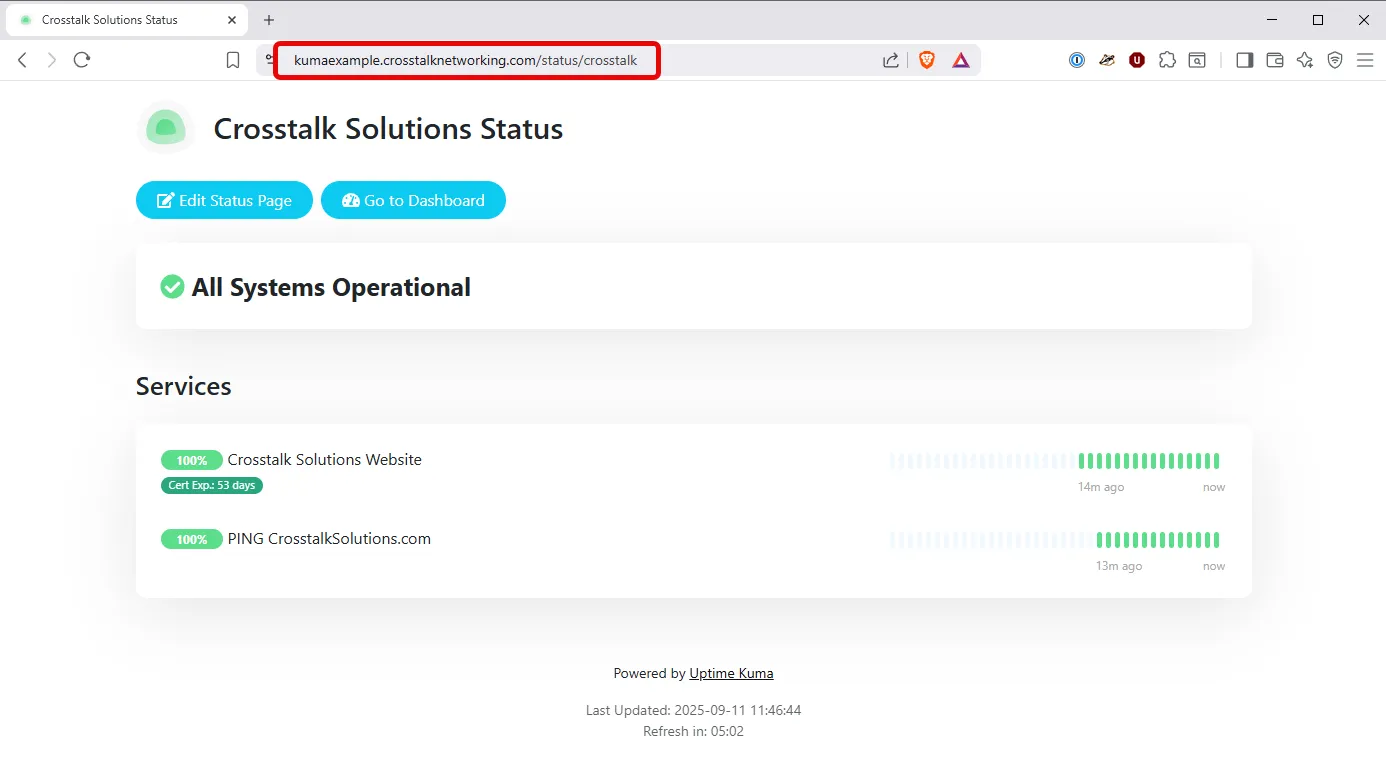
Part 6: Firewall rules
Since our server is exposed to the Internet through Digital Ocean, let’s use the ufw firewall to set up some simple rules.
I’m going to lock the server down so that only HTTP/HTTPS (ports 80/443) are open (80 is used for Let’s Encrypt certificate renewals), and then SSH port 22 is open, but locked down to my WAN IP address.
Log back into your server’s SSH console and run the following commands:
sudo ufw allow from 1.2.3.4 to any port 22
sudo ufw allow 443/tcp
sudo ufw allow 80/tcp
sudo ufw enable
Be sure to replace 1.2.3.4 with your own WAN IP address or subnet range in that first command there.
That’s it! Enjoy your new Uptime Kuma server!
If you need any help setting up a server like this, be sure to contact Rogue Support and our expert technicians are standing by to assist!
Or you can always buy me a coffee (or a beer)!